
AI-Driven Network Detection & Response
Detect hidden network threats with AI-powered network detection and response across hybrid enterprise environments.
Overview
Modern cyberattacks often bypass traditional perimeter defenses and operate quietly within enterprise networks. Without deep visibility into network traffic, detecting advanced threats such as lateral movement, command-and-control communication, or data exfiltration becomes difficult. Atlas United's AI-Driven Network Detection and Response (NDR) service analyzes network traffic using artificial intelligence and behavioral analytics to identify suspicious activity in real time. By continuously monitoring network environments, Atlas United enables organizations to detect advanced threats early and respond before they escalate into major security incidents.
Customer challenge
Organizations struggle to detect stealthy threats operating within networks due to limited visibility and traditional security limitations.
Hidden network threats
Advanced attackers operate quietly within networks using stealth techniques that evade traditional security controls.
Lack of network visibility
Security teams often lack deep visibility into east-west traffic across internal network environments.
Lateral movement attacks
Once inside the network, attackers move laterally to access additional systems and sensitive data.
Delayed threat detection
Traditional tools may fail to detect suspicious behavior until after damage has occurred.
AI-powered network threat detection
AI-based threat detection
Deep network visibility
Lateral movement detection
Real-time threat response
Threat intelligence integration
Improved incident investigation
Our solutions
Atlas United's AI-Driven NDR leverages advanced network detection technology to analyze network traffic, detect abnormal behaviors, and identify advanced cyber threats across enterprise and hybrid environments.
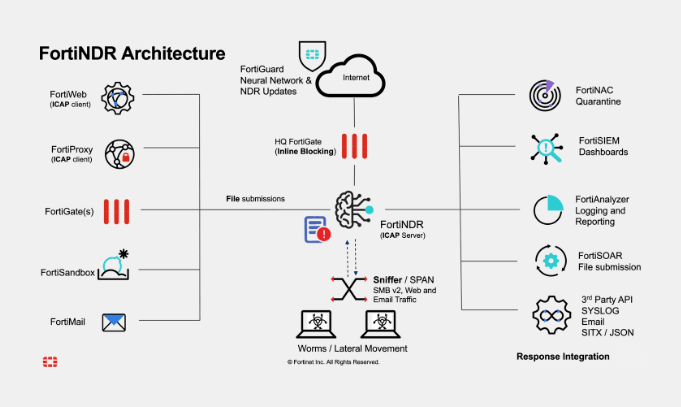
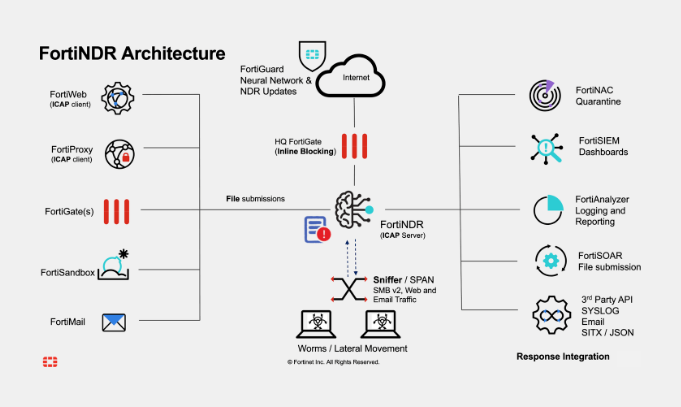
- Monitor network traffic using AI-based behavioral analytics to detect suspicious activity.
- Identify lateral movement, command-and-control communications, and abnormal network behavior.
- Provide detailed threat intelligence and automated response recommendations.
Highlights
- AI-based network threat detection
- Behavioral traffic analysis
- Advanced threat intelligence
Where AI-Driven NDR makes the difference
Critical infrastructure
Detect advanced threats targeting industrial networks and operational technology environments.
Financial institutions
Monitor internal network traffic to detect fraud attempts and unauthorized system access.
Telecommunications
Protect complex network infrastructure from advanced persistent threats and data exfiltration.
Large enterprise networks
Monitor high-volume network environments for hidden cyber threats and suspicious activity.
Why choose Atlas United AI-Driven NDR
Advanced AI-powered analytics
Leverage machine learning models to detect hidden threats within network traffic.
Deep network traffic visibility
Gain comprehensive insight into internal network communications and suspicious behaviors.
Proactive threat detection
Identify advanced threats early before attackers can escalate or exfiltrate sensitive data.
Expert security monitoring
Atlas United cybersecurity specialists analyze network threats and respond rapidly to potential incidents.
Want more?
Strengthen your threat detection and network security with Atlas United's advanced managed cybersecurity services.

EDR/XDR
Detect and respond to advanced endpoint threats using behavioral analytics and automated response.
Cyber Defense Center (SOC)
24/7 monitoring, threat detection, and incident response across enterprise environments.
Secure SD-WAN
Secure and optimize connectivity across branch offices, data centers, and cloud environments.
DDoS Shield
Protect internet-facing applications from large-scale distributed denial-of-service attacks.
Secure Web Gateway
Protect users from malicious websites, phishing attacks, and unsafe internet activity.
Container & Kubernetes Security
Secure containerized applications and Kubernetes clusters from vulnerabilities and runtime threats.
Technical Assessment
Identify vulnerabilities, misconfigurations, and security risks across your enterprise infrastructure.
Let's talk about your business security strategy
Have a question or need more information? Get in touch and our cybersecurity experts will assist you.